
DDoS protection · Now in beta
Attacks never reach
you.
Stopped at your edge — on a NuajBridge, your Linux servers or your MikroTik routers.
Free during the beta.
It begins
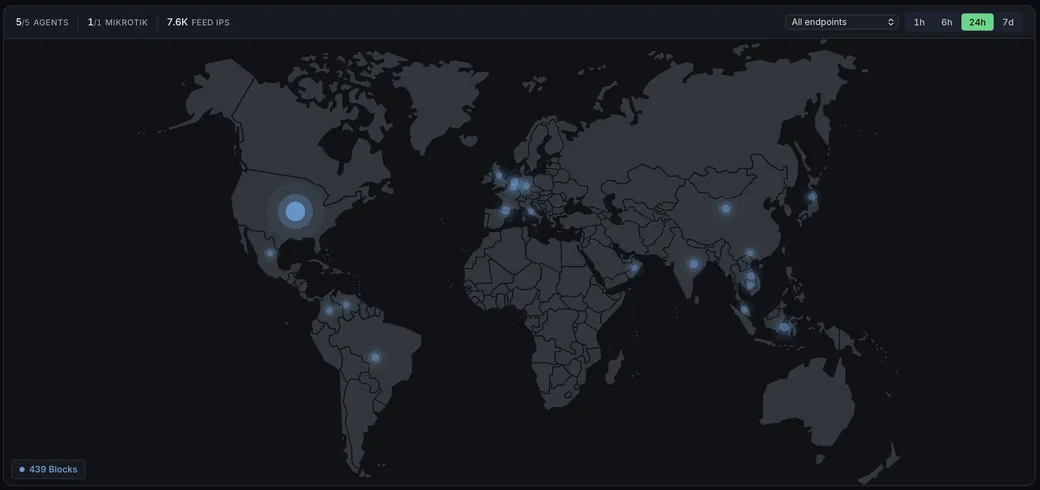
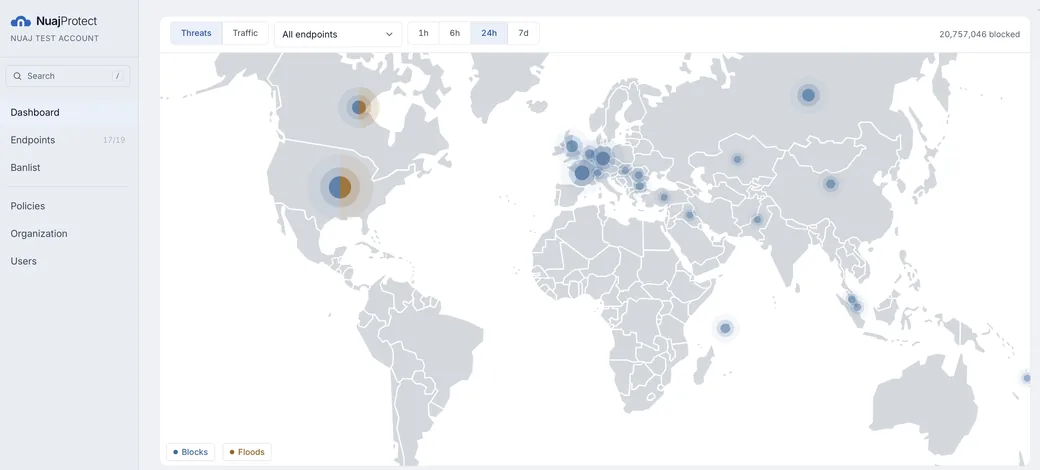
An attack begins.
You see it at once.
Every edge you protect reports to one live map.
It is stopped
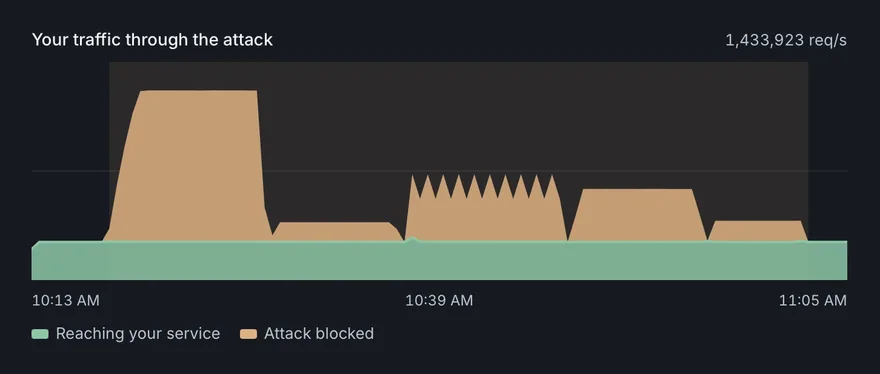
Five waves.
Your traffic never noticed.
Forty-five minutes of attack, stopped at the edge. Everything you serve ran flat beneath it.
It is explained
Then the whole story.
In one report.
How long it lasted, what was blocked, and every network it came from.
Duration
Blocked
Sources
Networks
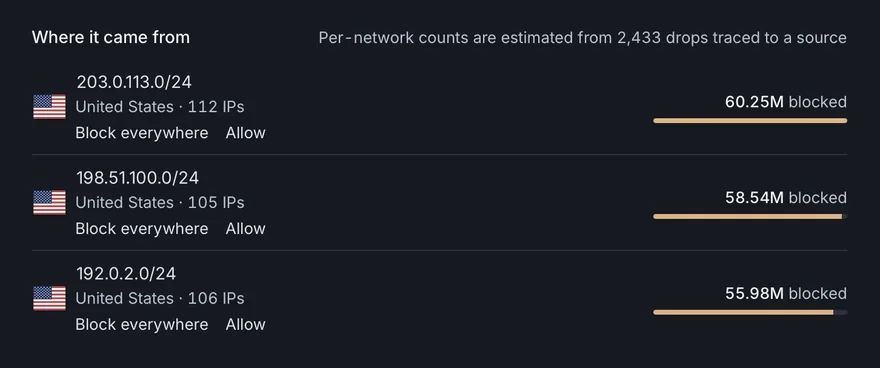
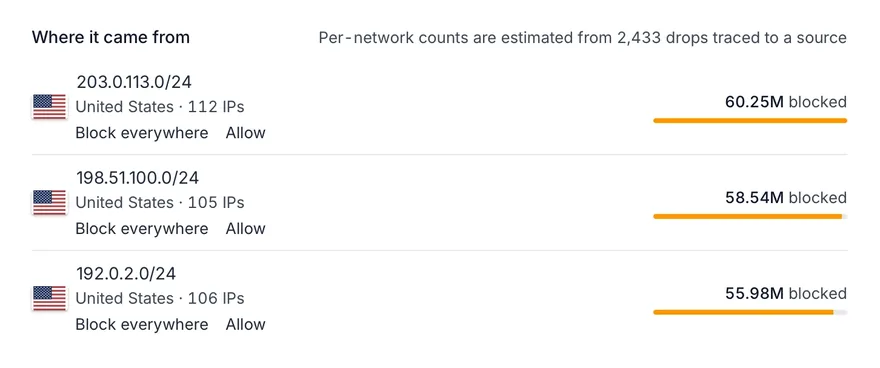
A 45-minute test attack on the NuajProtect bench, October 2026.
You decide
Your call.
On every edge at once.
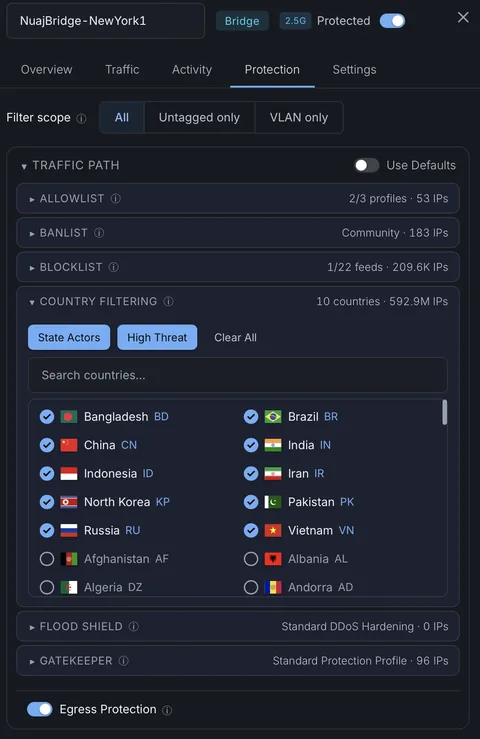
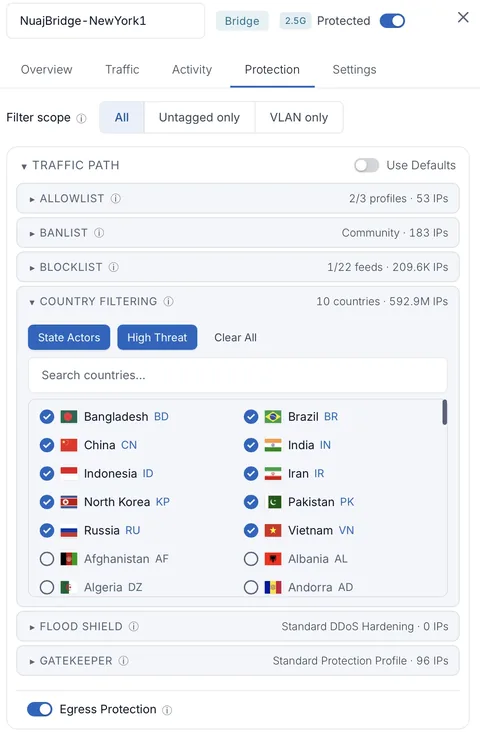
Block a network everywhere with one click. Choose the feeds and countries each edge enforces.
How it works
Every connection.
Checked before it lands.
What one edge learns, every edge enforces.
Known threats, blocked
Live threat feeds and your own list stop botnets and scanners.
New attacks, caught
A source turns hostile. Every edge blocks it.
DDoS, absorbed
Floods are shed at the edge, judged against your normal.
Regions, controlled
Choose which countries reach which services.
Probing, stopped
Scans and brute force give a source away.
Trusted, untouched
The people and systems you trust pass untouched.
Where it runs
Three ways to run it.
One account.
A NuajBridge in front of a whole network, or the servers and routers you already run.
Appliance · Coming soon
NuajBridge
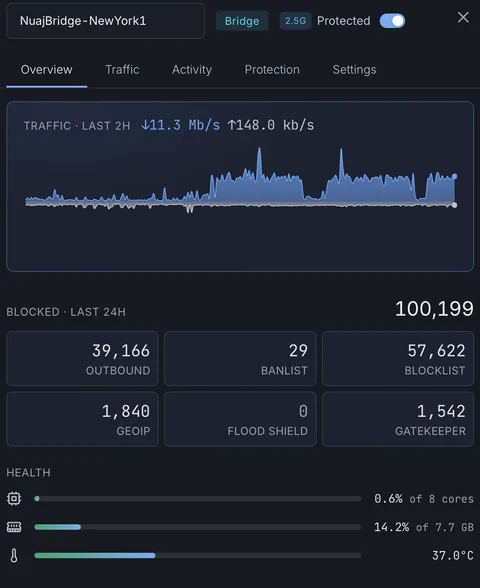
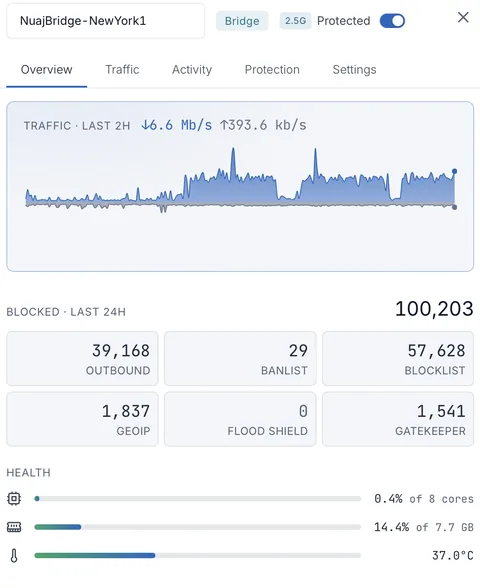
Between your internet connection and your router. Nothing to install, nothing to attack.
- 2.5G and 25G models
- Every packet, in and out
- 99.8% of your traffic delivered during an attack
On your servers
Linux
One binary on the server. Hostile traffic stops before it reaches your website, mail or DNS.
- Web servers, APIs and reverse proxies
- Mail, DNS, VPN and game servers
- Or in front of them, as a relay
- Your applications can report attackers
On your routers
MikroTik
One generated script, pasted into the router’s terminal. Its own firewall does the enforcing.
- RouterOS 7.13 or later
- IPv4 and IPv6
- Enforced by RouterOS’ own firewall
Each one sits in front of what it protects, behind it, or invisibly in the path. See which goes where
How it fits together
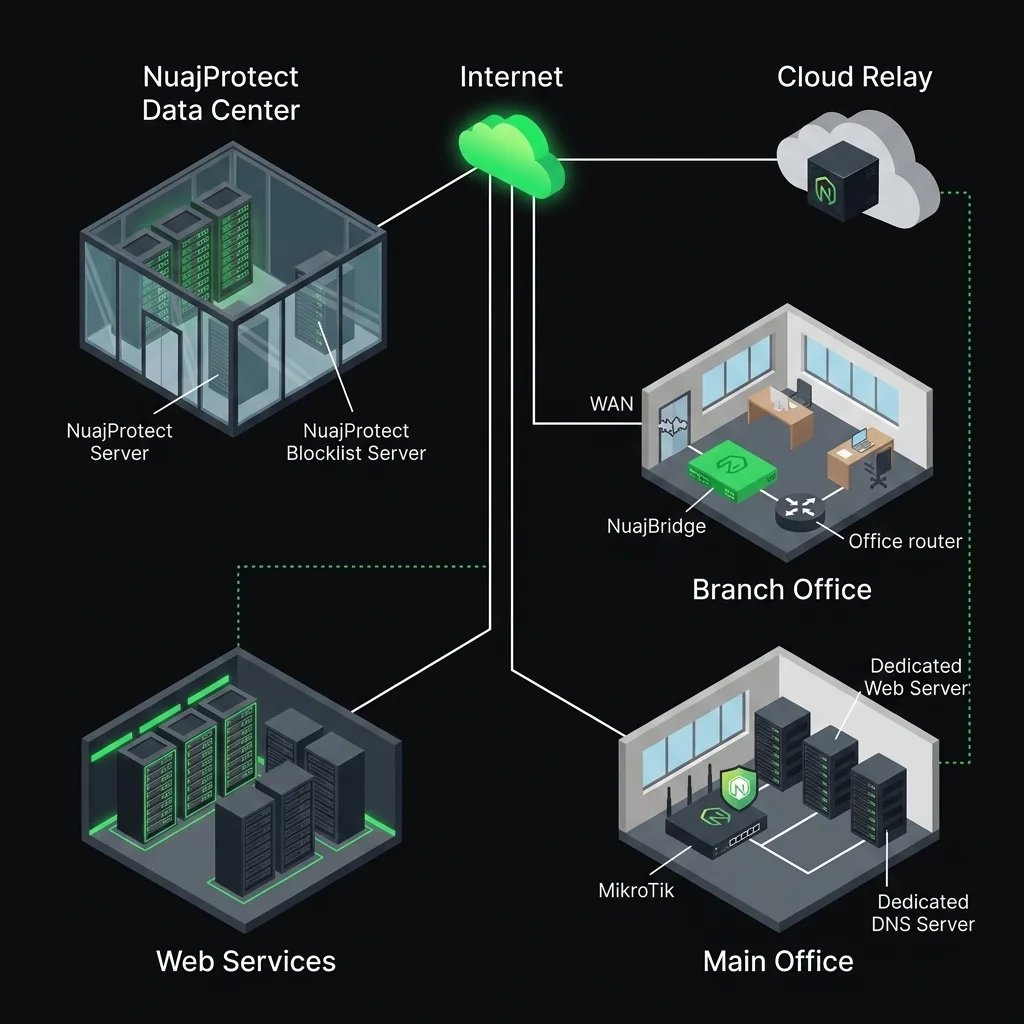
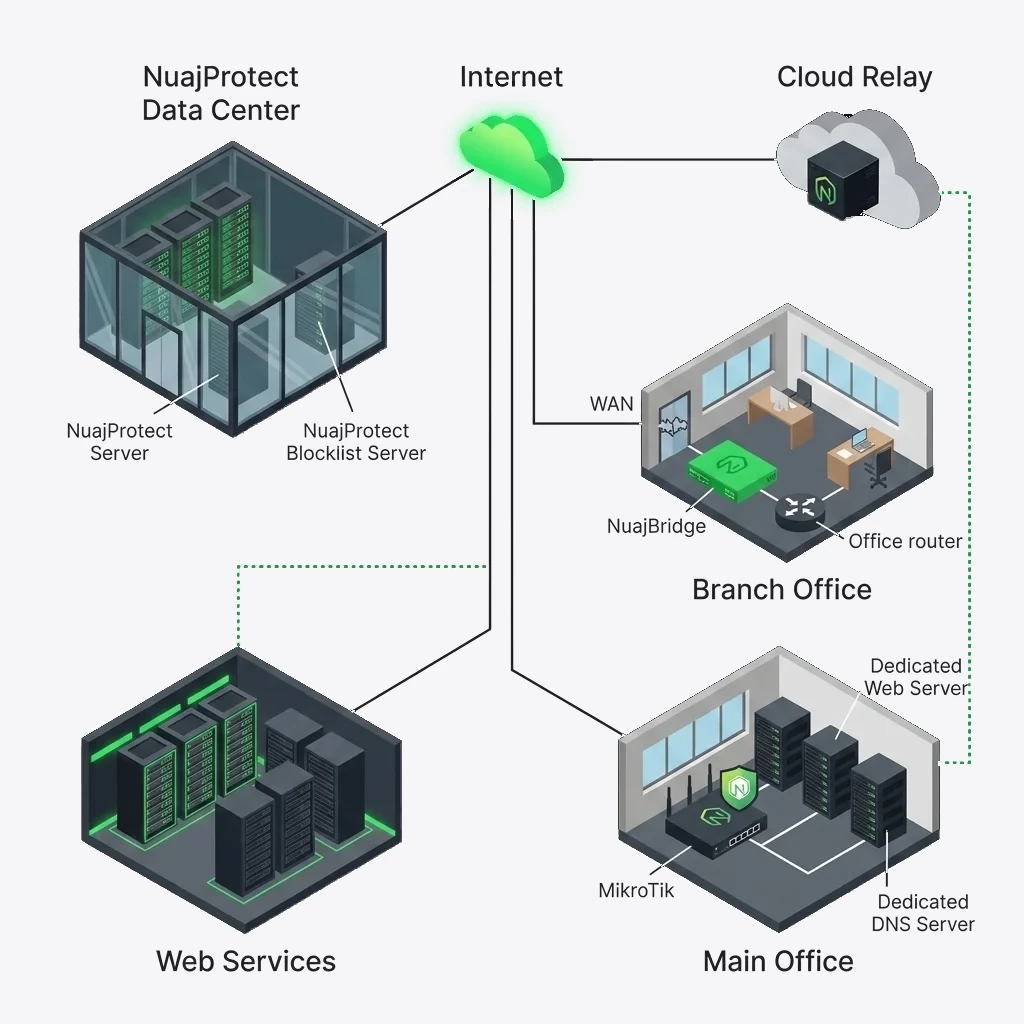
Servers, routers, remote services and whole network edges, protected from one central policy.
Security
Shared protection.
Without shared risk.
Every location learns from every attack, and stays yours alone.
Communications
Encrypted end to end
Outbound-only and encrypted. No open port for an attacker to reach.
Authentication
Multi-factor authentication
Authenticator apps, passkeys, SMS and email. Built in, not an add-on.
Access control
Role-based permissions
Six roles, from Account User to Super Admin, for every tenant.
Notifications
Real-time alerts
Email and SMS the moment an attack starts or an edge goes quiet.
Integration
Your apps can fight back
The failed logins and scraping your apps see become blocks on every edge.
Flexibility
Policy profiles
Standard profiles, or your own per edge, site or customer.
Prefer it in-house? NuajProtect runs fully self-hosted, even air-gapped. Talk to us about self-hosting
Where it started
Built by operators.
Proven in production.
NuajProtect defends the networks of Halton Data Center, a Canadian colocation and cloud provider. Every release runs there first. Visit Halton Data Center
At a glance
NuajProtect,
at a glance.
NuajProtect is edge threat protection for servers, routers and whole networks: network security software, and a network security appliance, that removes hostile traffic before it reaches what you run — infrastructure already known to be attacking, from a live global feed, and everything nobody has classified yet, worked out on the spot. Every decision is enforced in the traffic path, with no proxy. It runs on the Linux servers you already own, on MikroTik routers, and on the NuajBridge inline appliance.
| Product type | Edge threat protection — network security software and a network security appliance |
|---|---|
| What it does | Blocks malicious inbound traffic at the network edge: known hostile sources, floods, port scanners, repeat offenders and application-reported abuse |
| Runs on | Linux servers (single static binary under systemd, x86-64 and arm64) · MikroTik RouterOS 7.13+ · NuajBridge appliance, 2.5G and 25G, coming soon |
| Enforcement | Accelerated filtering on Linux and NuajBridge; RouterOS firewall on MikroTik. No proxy, no extra routing hop |
| Placement | Sentry (protects the host it runs on) · Relay (protects what is behind it, directly or over GRE, WireGuard or IPsec) · Bridge (transparent, inline, no address to attack) |
| Addressing | IPv4 and IPv6, first-class in both |
| Control plane | Managed SaaS, or self-hosted for data sovereignty and air-gapped networks |
| Availability | In beta, and free to join. NuajBridge appliances are coming soon |
| Licence | Proprietary. End User Licence Agreement |
| Vendor | Nuaj Company Inc., Ontario, Canada |
Questions
Everything you need
to know.
What is NuajProtect?
What platforms does NuajProtect run on?
How is NuajProtect different from a traditional firewall?
Will NuajProtect slow down my network?
Is NuajProtect self-hosted or SaaS?
How do I get access to NuajProtect?
How do I stop a DDoS or UDP flood at my network edge?
Does NuajProtect filter IPv6 as well as IPv4?
What happens if NuajProtect loses contact with the control plane?
How is NuajProtect different from Fail2ban or CrowdSec?
Is NuajProtect a cloud DDoS protection service?
Get started
Stop the attacks.
Keep control.
Start on the servers and routers you already run — the service is free through the beta. Add a NuajBridge when you want the whole network covered.